Hackers Steal Text and Call Records of ‘Nearly All’ AT&T Customers
In one of the most significant data breaches in recent history, hackers stole AT&T customers’ call and text metadata spanning several months. Hackers broke into a…
Blog
Long-form investigations from the Hudson Rock research team. Filter by topic to narrow down.
In one of the most significant data breaches in recent history, hackers stole AT&T customers’ call and text metadata spanning several months. Hackers broke into a…
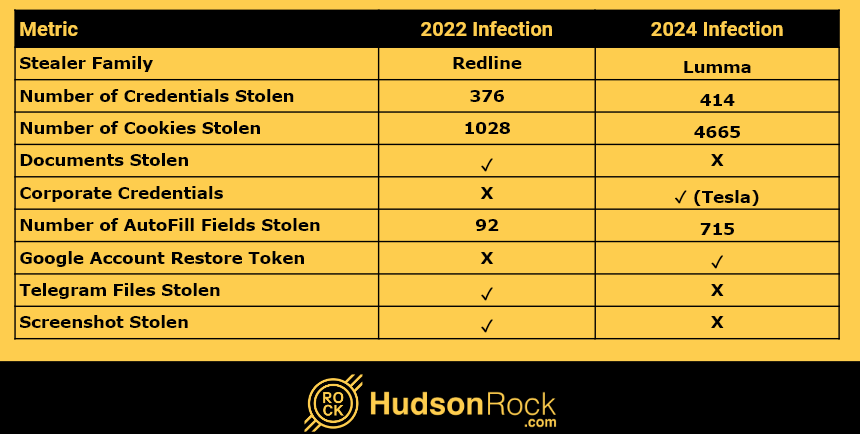
Having your data stolen once is bad enough, but for some people, it happens repeatedly. Infostealer infections are not a new phenomenon in the cybersecurity world,…
Executive Summary On Tuesday, June 18th, 2024, Rapid7 initiated an investigation into suspicious activity in a customer environment. Our investigation identified that the suspicious behavior was…
A potential shift in Infostealers might be happening again. Traditionally, teams of cybercriminals develop an Infostealer family (variant) such as Redline, Lumma, Raccoon, etc., and rent…
AU10TIX, a company that verifies the identities of TikTok, Uber, and X users, sometimes by processing photographs of their faces and pictures of their drivers’ licenses,…
Affected Platforms: Microsoft WindowsImpacted Users: Microsoft WindowsImpact: The stolen information can be used for future attackSeverity Level: High The past few years have seen a significant increase in the number…
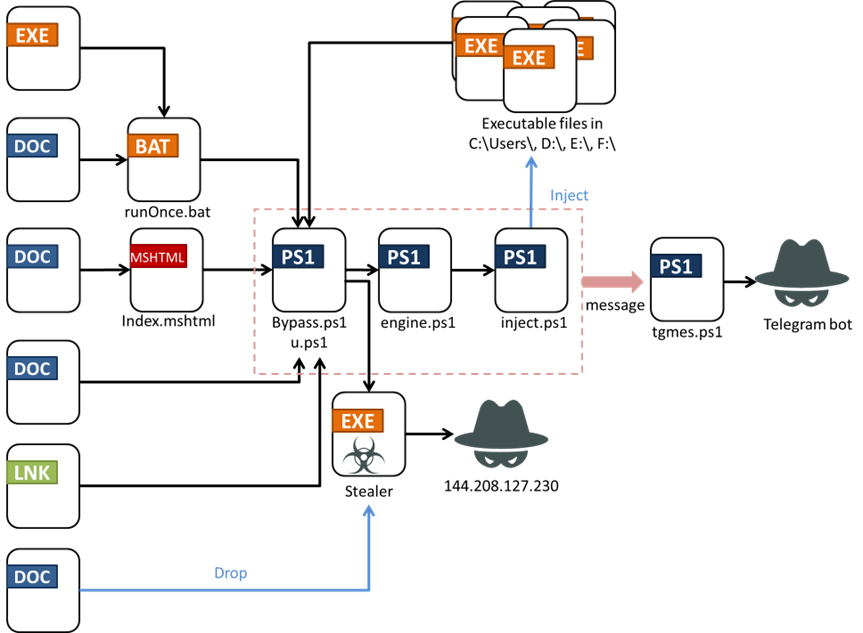
Case Summary It was a quiet Monday morning in March 2024 when the EDR researchers with our Trellix Advanced Research Center identified an interesting sequence of…
Learn about Infostealers with actual real life breaches caused by Infostealer infections with Leonid Rozenberg, Hudson Rock's Head of Partnerships & Integrations. To discover how your…
Infostealers commit close to the perfect crime. They sneak into your computer, grab your logins, passwords, and anything of value, and then delete themselves on the…
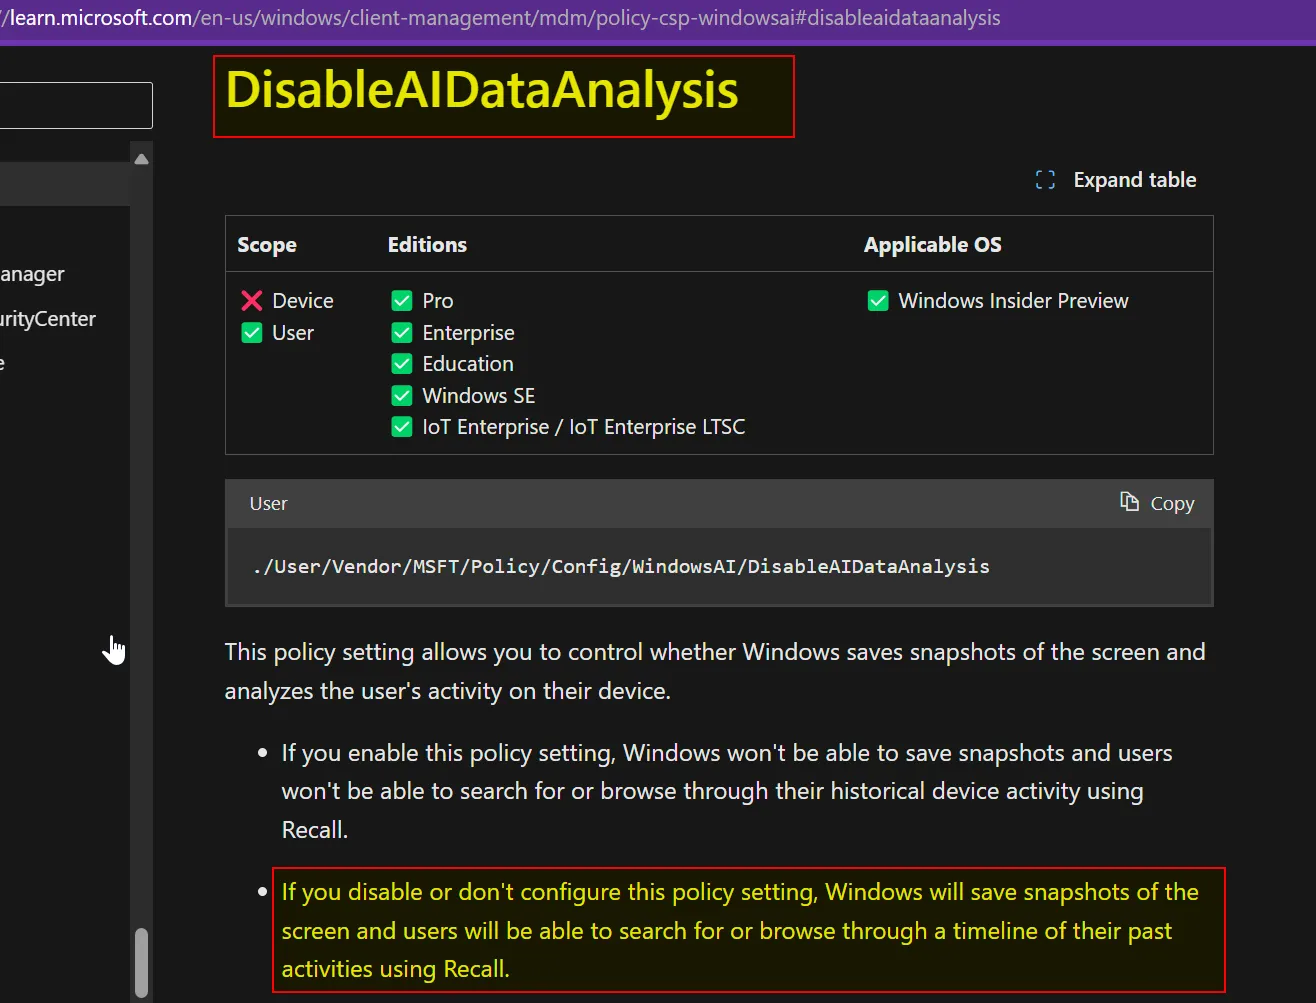
I wrote a piece recently about Copilot+ Recall, a new Microsoft Windows 11 feature which — in the words of Microsoft CEO Satya Nadella- takes “screenshots” of…
EXECUTIVE SUMMARY At CYFIRMA, we are committed to offering up-to-date insights into prevalent threats and tactics employed by malicious actors who target organizations and individuals. The…
The adversaries use the open-source SapphireStealer to create their own Infostealer malware for collecting employee authentication data from Russian companies. Since March 2024, the BI.ZONE Threat Intelligence team…