Chae$ Chronicles: Version 4.1 Dedicated to Morphisec Researchers
In ongoing efforts to monitor and analyze emerging cyber threats, Morphisec Threat Labs has recently turned its focus to Chae$ 4.1, an update to the Chaes…
Article Type
In ongoing efforts to monitor and analyze emerging cyber threats, Morphisec Threat Labs has recently turned its focus to Chae$ 4.1, an update to the Chaes…
Cryptocurrency on-chain sleuth, ZachXBT, alerted the cryptocurrency community today that several notable organizations such as CoinTelegraph and WalletConnect are being used to send phishing messages through…
A month ago, we discovered some cracked apps circulating on pirating websites and infected with a Trojan proxy. The malicious actors repackaged pre-cracked applications as PKG files with…
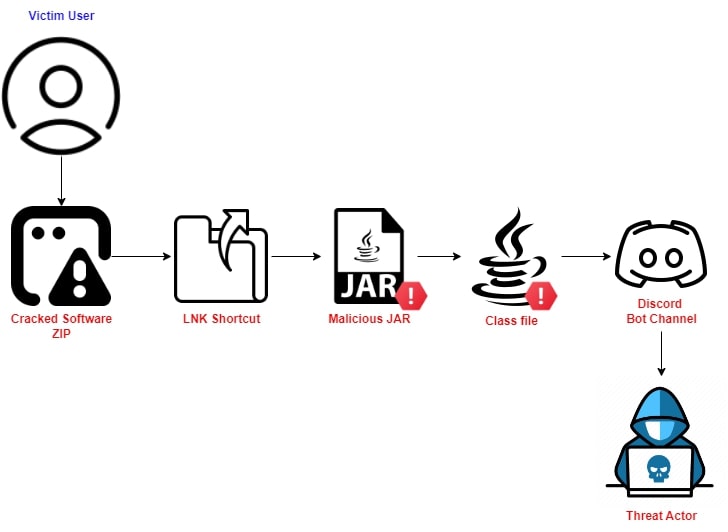
Executive Summary: In mid-November 2023, Trellix Advanced Research Center team members observed a Java-based stealer being spread through cracked software zip files using JDABuilder Classes to…
We have been reporting on the rise of infostealers targeting macOS since early last year, but threat actors show no signs of slowing down. Throughout last…
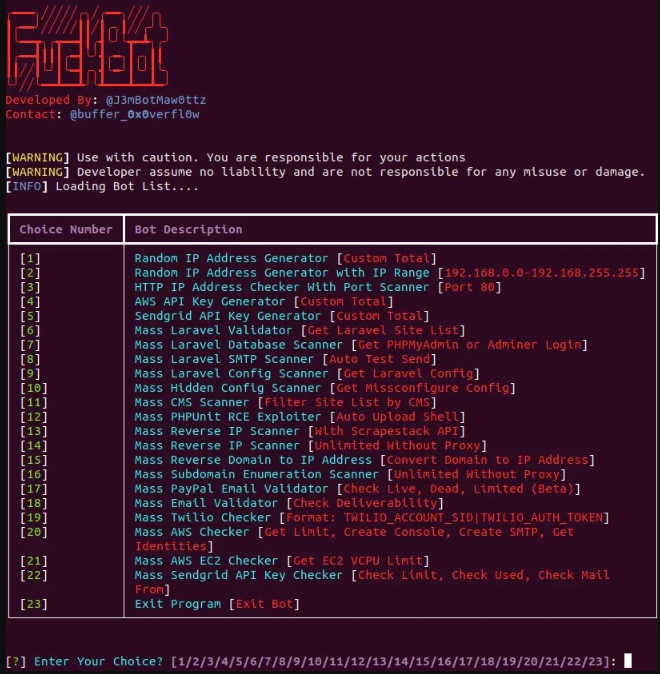
Executive Summary FBot is a Python-based hacking tool distinct from other cloud malware families, targeting web servers, cloud services, and SaaS platforms like AWS, Office365, PayPal,…
Last year, we documented malware distribution campaigns both via malvertising and compromised sites delivering Atomic Stealer (AMOS) onto Mac users. This stealer has proven to be quite popular in the…
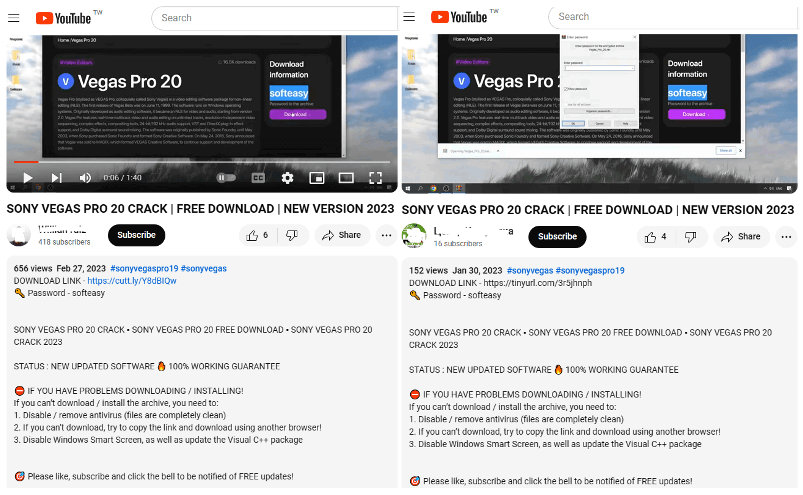
FortiGuard Labs recently discovered a threat group using YouTube channels to distribute a Lumma Stealer variant...
To completely understand what’s going on in the info stealers market which has been growing in the last years...
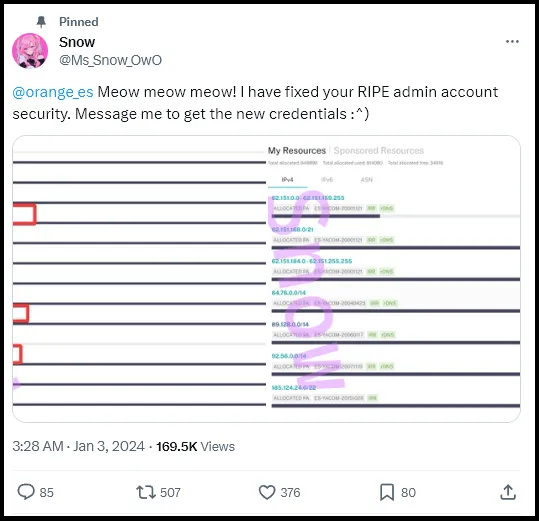
Using the stolen account, the threat actor modified the AS number belonging to Orange’s IP address, resulting in major disruptions...
This method can be applied to multiple other C2 servers that we come across on a daily basis to check for any security misconfigurations...
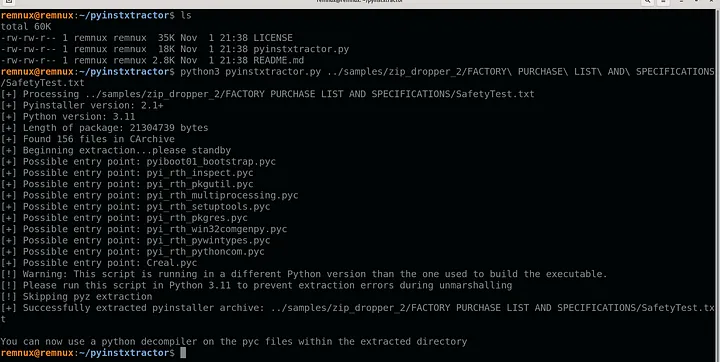
A ZIP/LNK payload and, with some luck, we will end up identifying the infostealer that is being dropped and its source code...