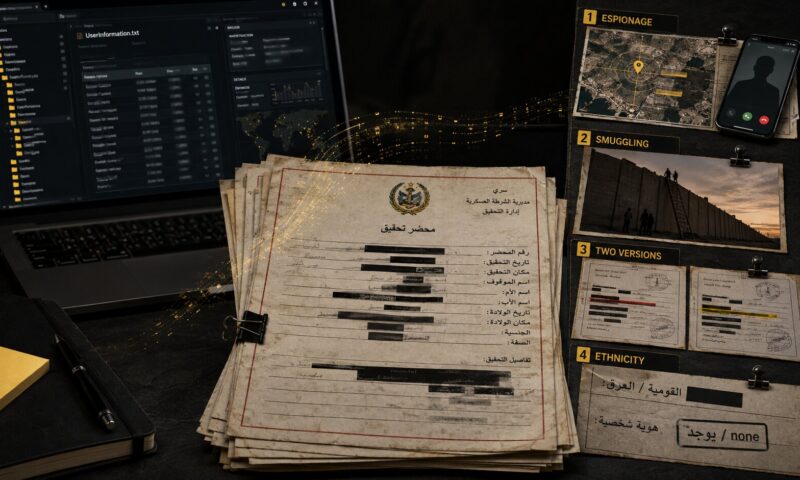
Inside a Syrian Interrogation Room: The Detainee Files an Infostealer Stole From a Military Police Unit
A single malware infection on one senior officer’s computer exposed the active caseload of a Syrian National Army military police unit
Topic
A single malware infection on one senior officer’s computer exposed the active caseload of a Syrian National Army military police unit
A compromised machine in Lebanon, belonging to a local ISIS cell commander - contained a very rare collection of explosive synthesis manuals, jihadist propaganda, and locally…
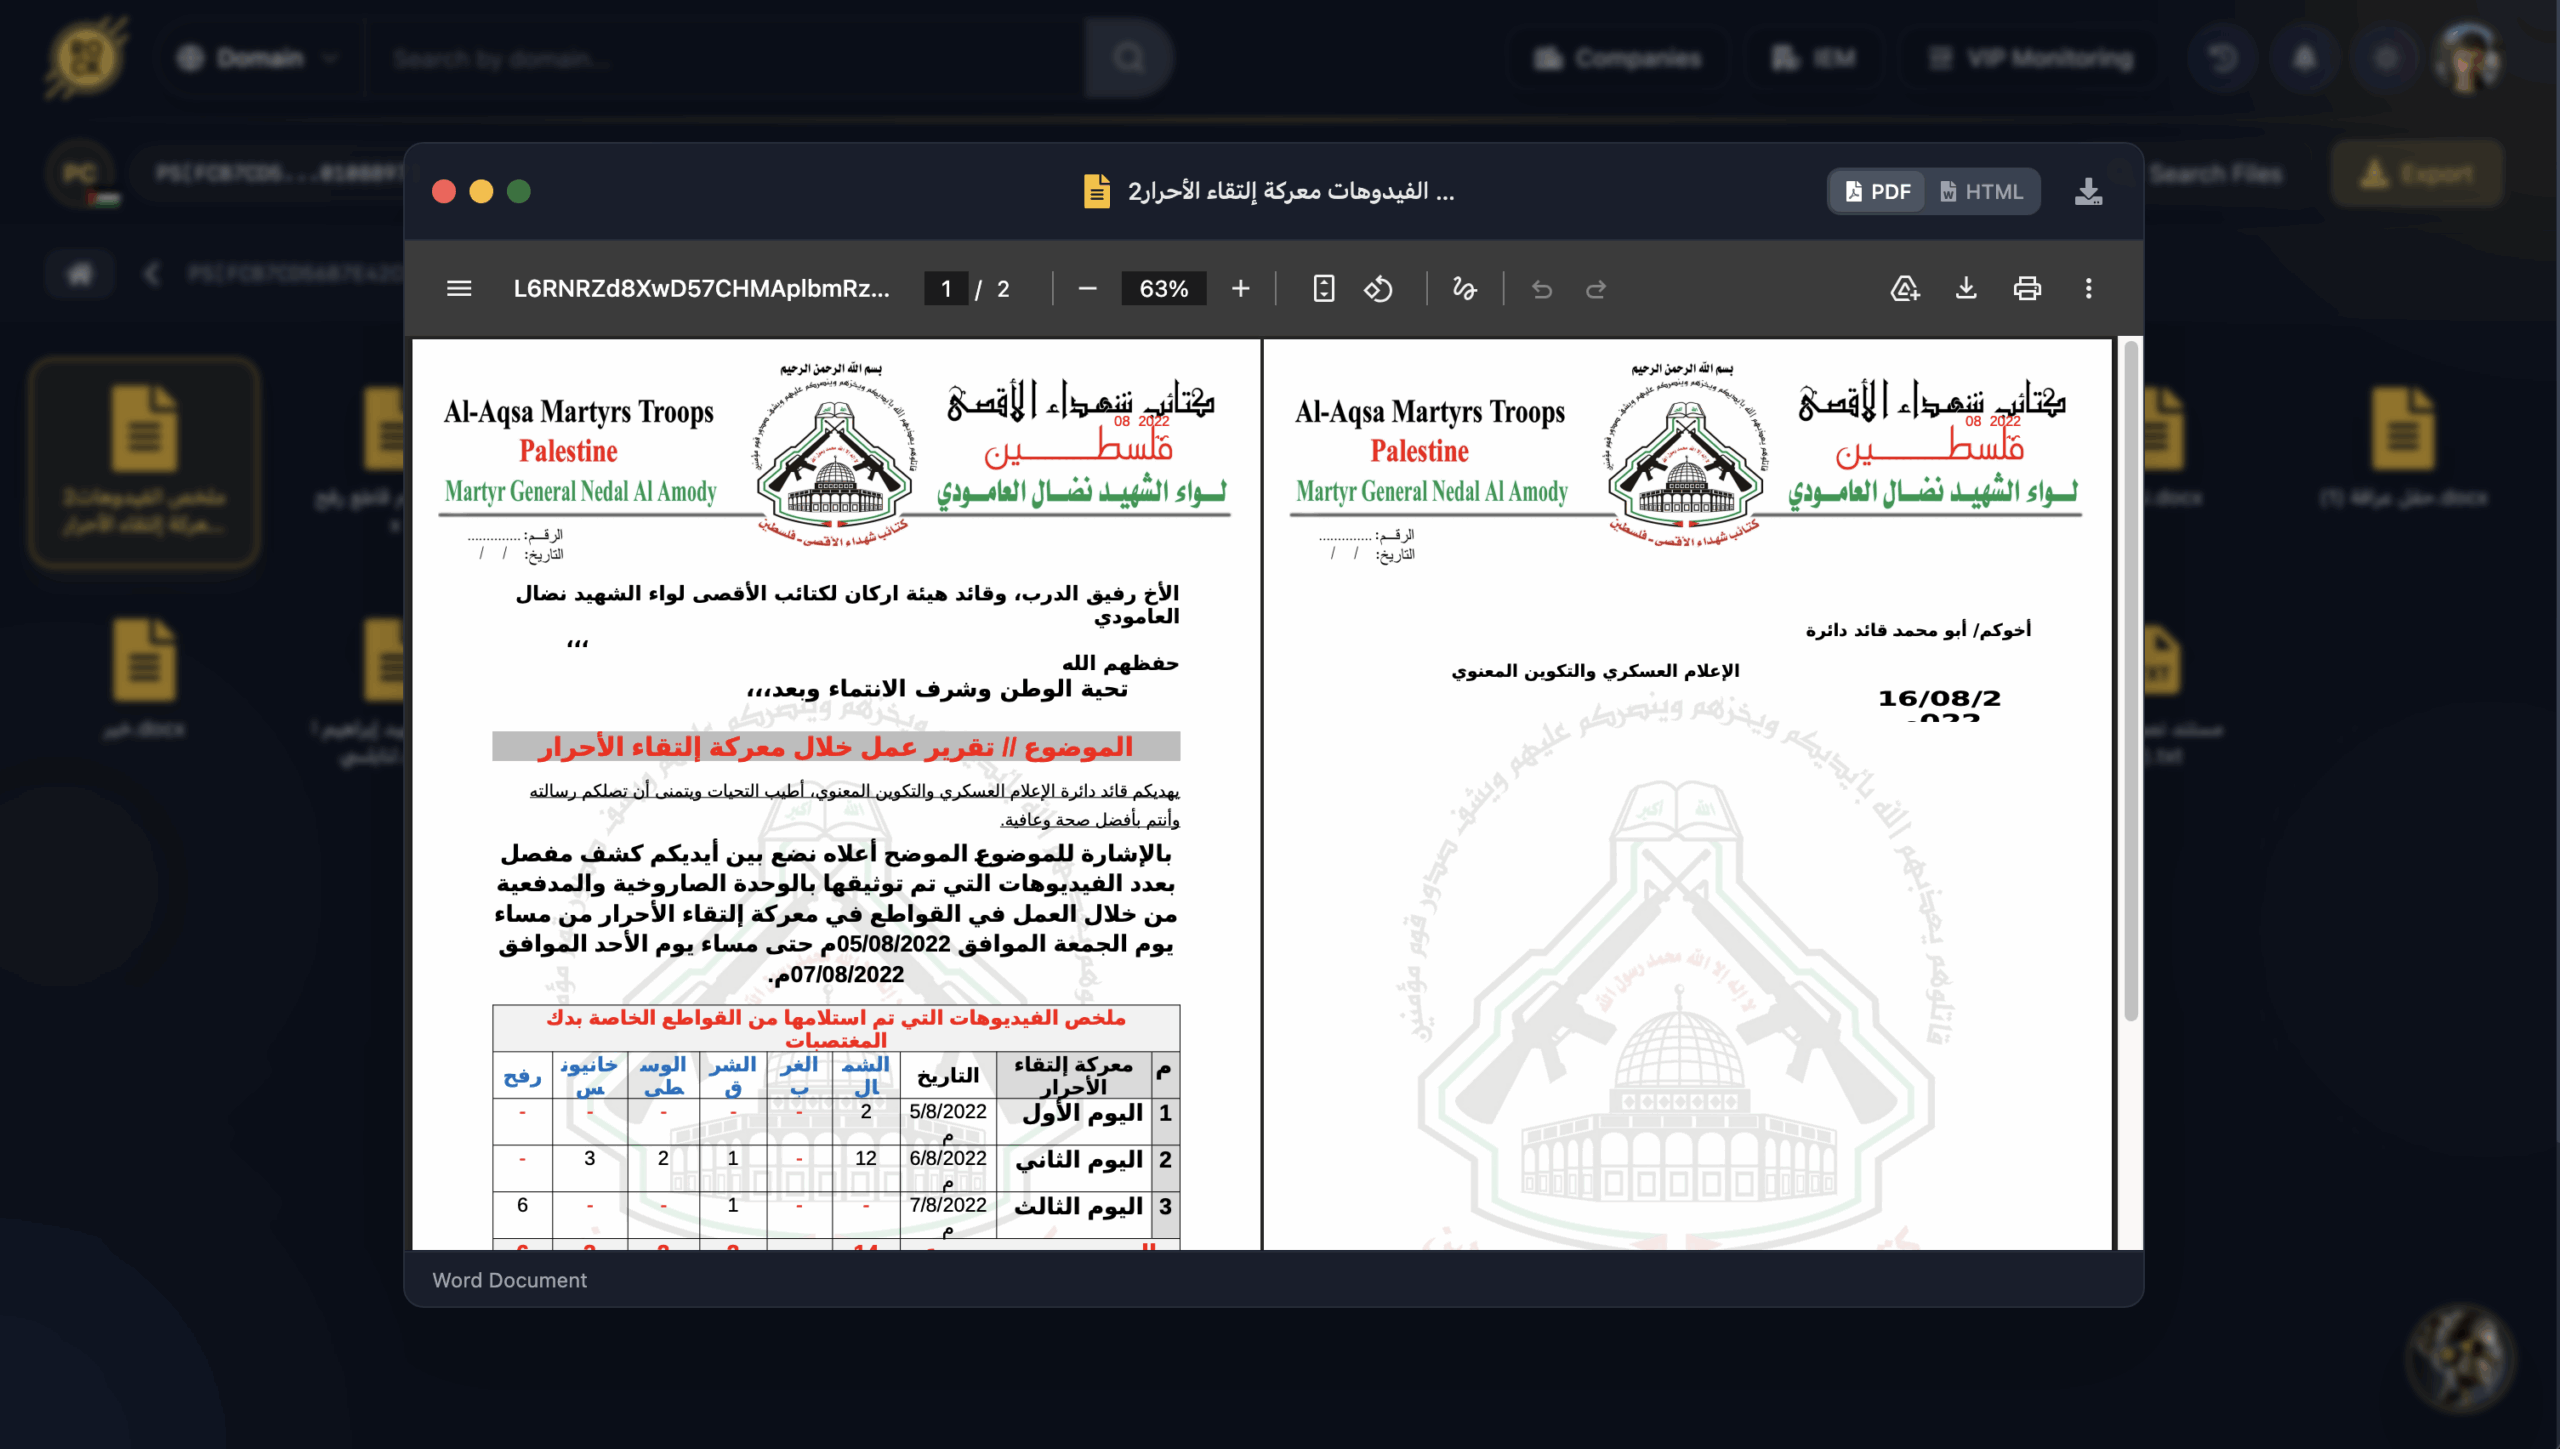
Hudson Rock researchers have recovered a full set of original internal documents from the Al-Aqsa Martyrs’ Brigades, exfiltrated from a compromised machine in the Gaza Strip
Analysis of a compromised machine in Deir al-Balah (Gaza Strip) has revealed a focused collection of documents attributed to Hamas’ Al-Qassam Brigades.
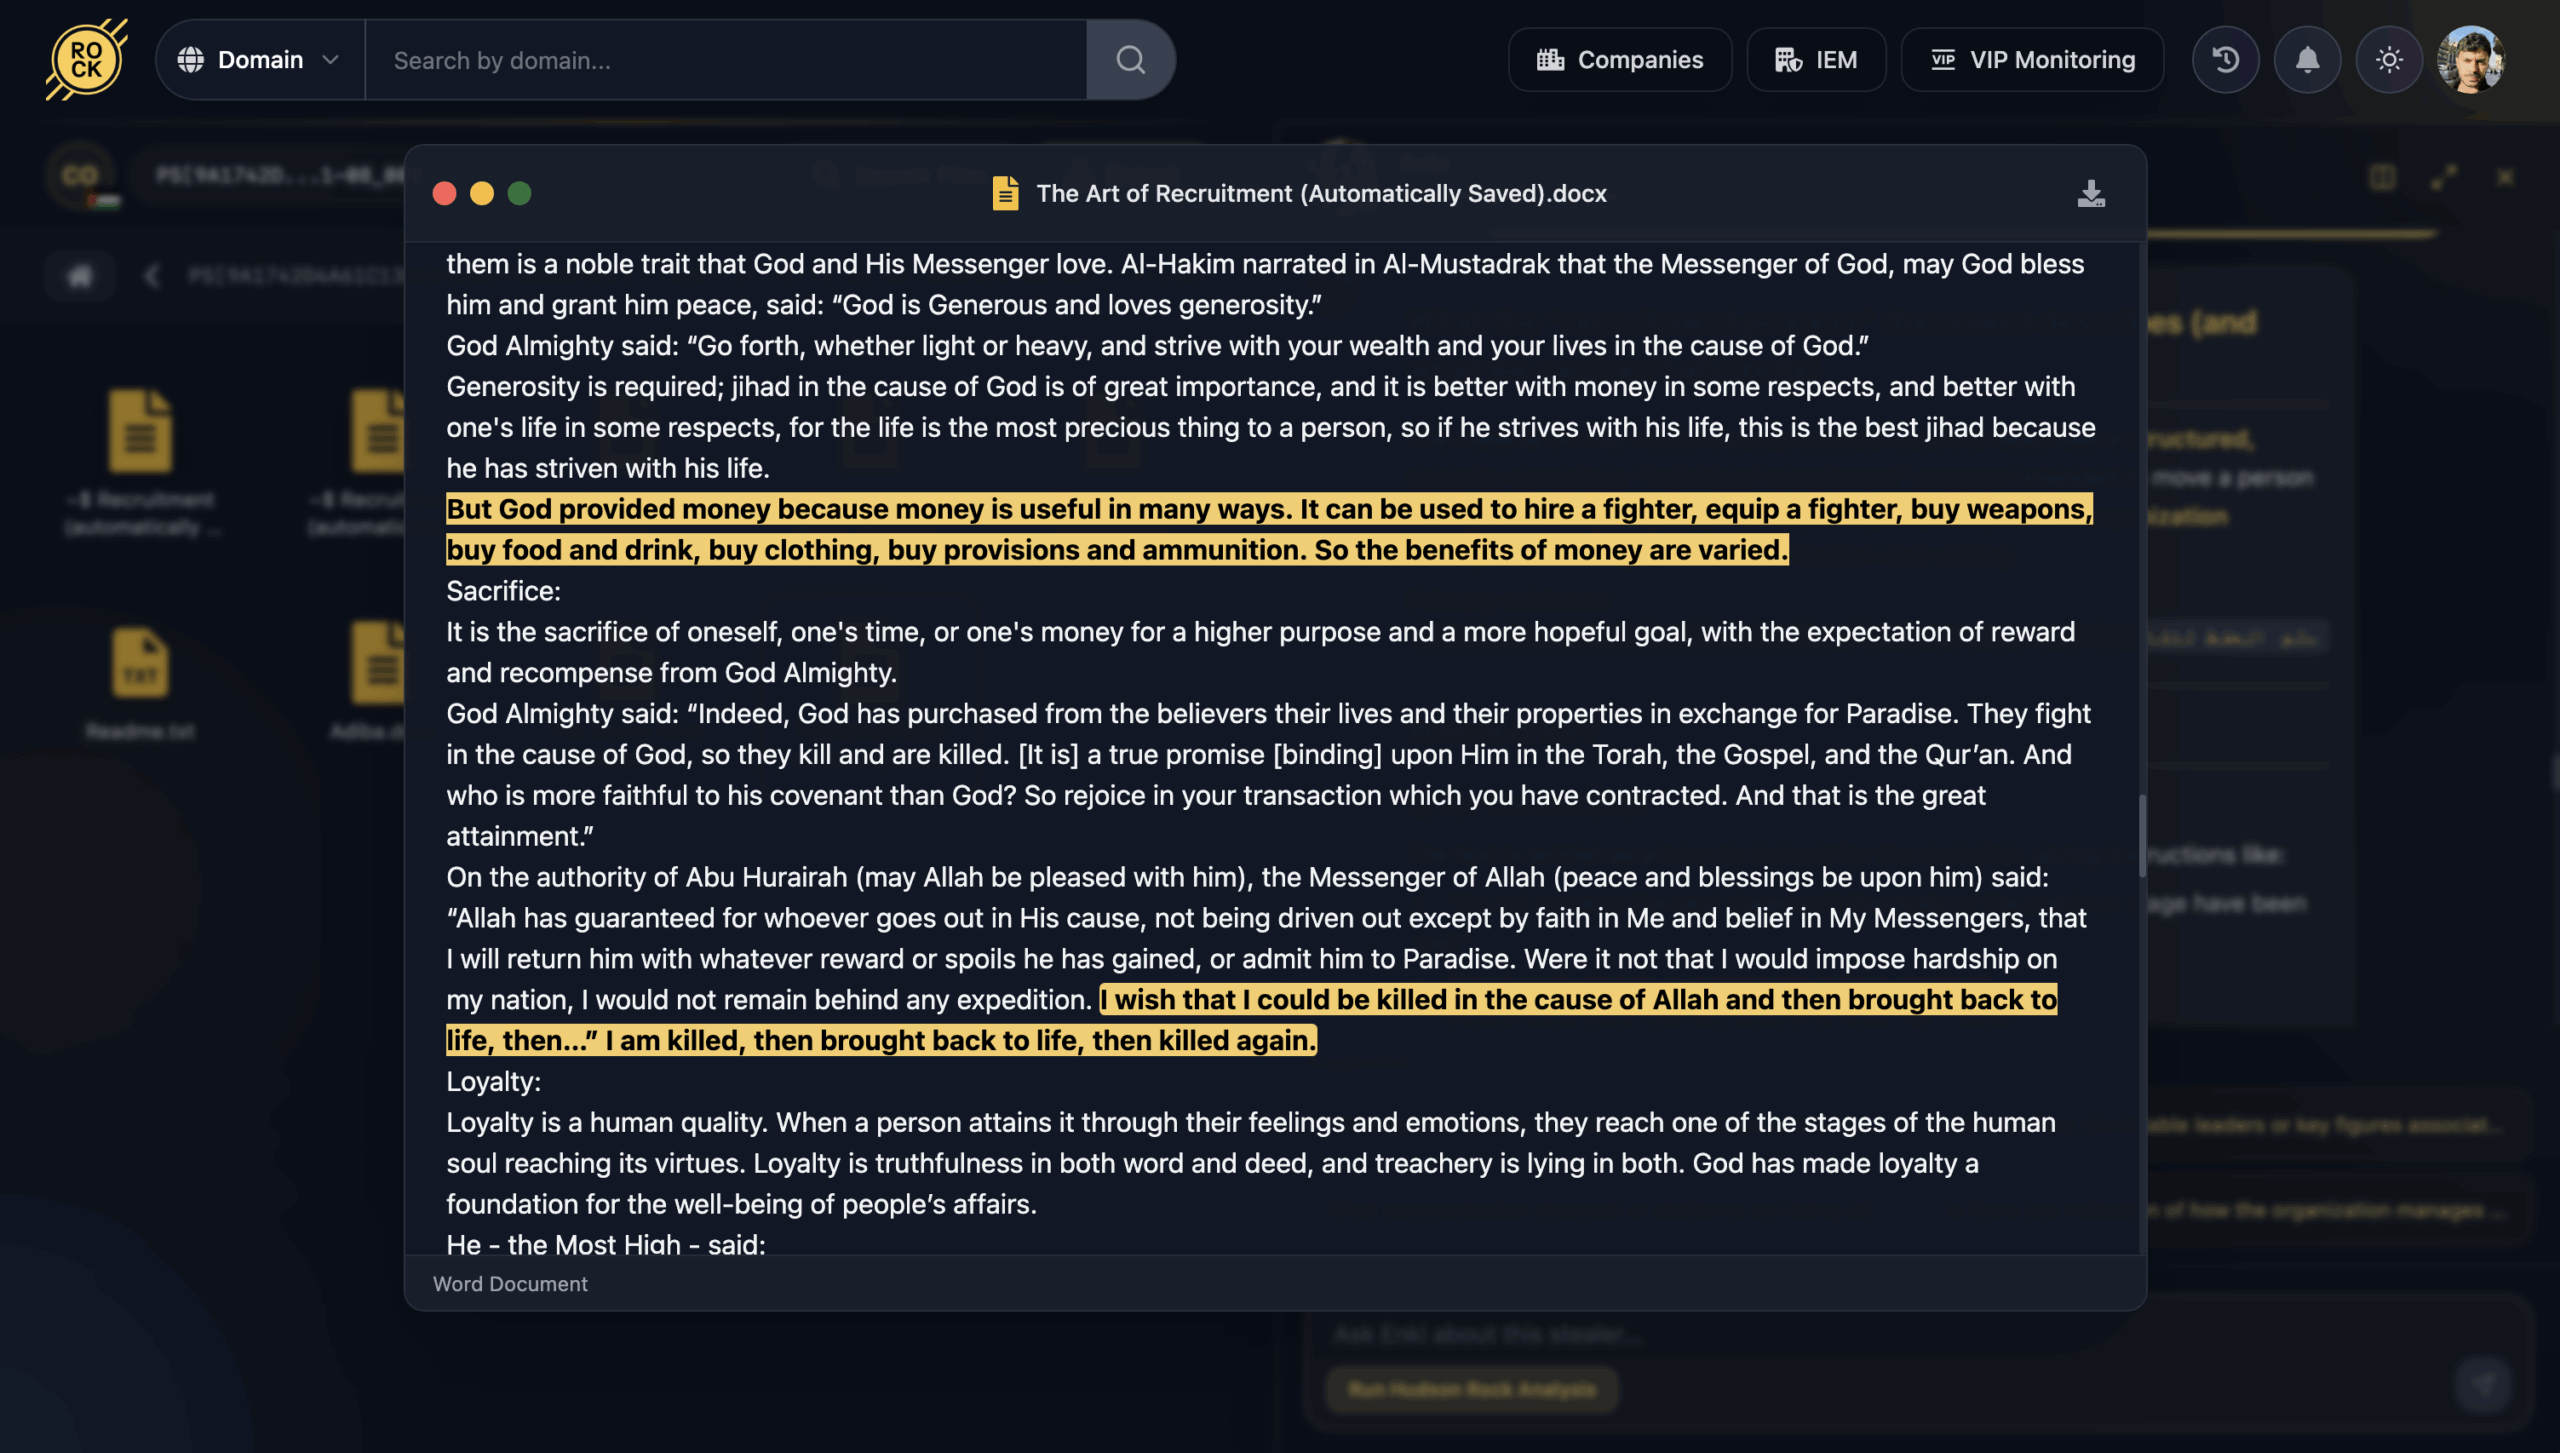
A comprehensive investigation conducted by the Hudson Rock team has identified a sophisticated Jihadist recruitment guide stored on an infostealer-compromised machine.
Hudson Rock is thrilled to announce the launch of CavalierGPT, the first-ever Infostealer Intelligence AI Bot designed to empower researchers with free access to data associated…
In this new episode of the mnemonic security podcast, Robby Peralta is joined by Leonid Rozenberg, a cybersecurity expert and dark web researcher at Hudson Rock,…
Disclaimer: Hudson Rock does not insinuate or imply responsibility or liability on behalf of any parties mentioned herein. The content is intended solely for informational purposes…
Interview with Malware Protection expert Leonid Rozenberg with Hudson Rock (www.hudsonrock.com) on exposing information stealers, protecting identities online, hackers who sell vulnerabilities, and how to know…
Learn about Infostealers with actual real life breaches caused by Infostealer infections with Leonid Rozenberg, Hudson Rock's Head of Partnerships & Integrations. To discover how your…
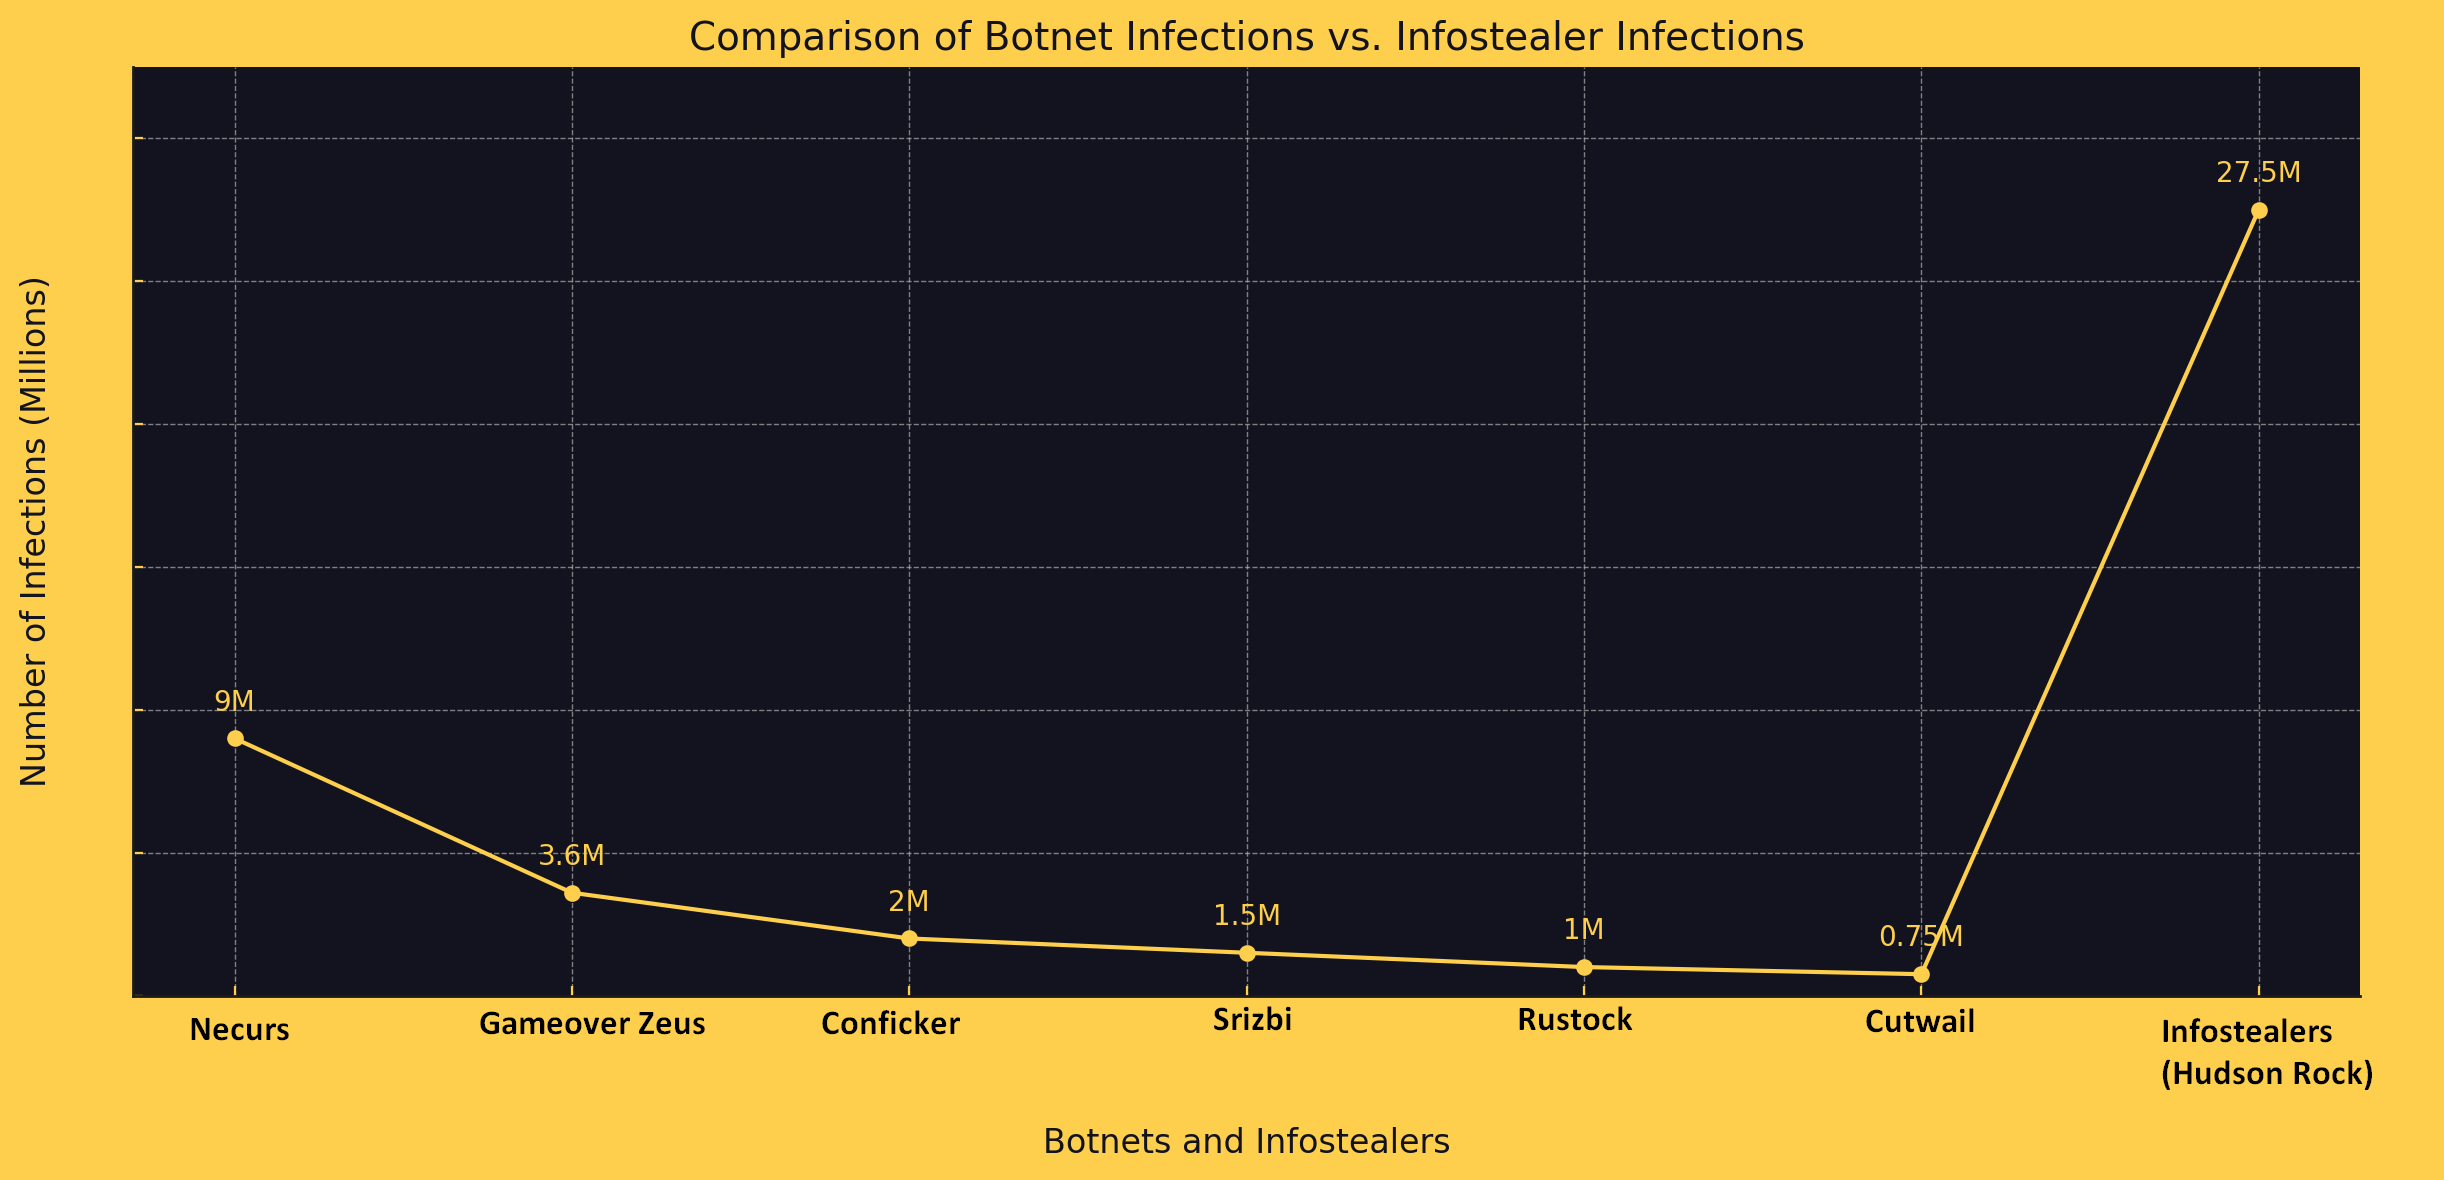
The landscape of cyber threats has been shifting dramatically in recent years, with a notable transition from traditional botnets to a more insidious form of malware:…
Introduction Hudson Rock recently shed light on how a compromised Citrix account without MFA was potentially used to deploy a devastating ransomware attack on Change Healthcare. This attack…